Skip to content
Mobile device, laptop and data cable on an examination desk
Mobile security & digital forensics

Signum CyberVerifiable evidence. Clear answers.

Independent technical examination of iOS and Android devices, connected accounts and known credential exposures. Methodical, documented and discreet — with a clearly structured technical report.

Authorised examinationDocumented methodologyZagreb · EU

Core capabilities

  • iOS and Android

    Examination of unlocked, client-owned devices.

  • Documented methodology

    Defined scope, chain-of-custody records and a repeatable procedure.

  • Evidential integrity

    Evidence manifest and cryptographic hash values where applicable.

  • EU-wide intake

    Devices are shipped to Zagreb following the instructions issued on case acceptance.

Services

Defined examination scopes at fixed prices

Each service has a scope defined in advance, a documented methodology and a written technical report that keeps observations separate from interpretation.

€790

Mobile-device forensic examination

Examination of available iOS or Android system, application, configuration and security artefacts: relevant diagnostic records, installed-app provenance, profiles, VPN and mobile-device-management configuration, permission state and available indicators, with incident-timeline correlation. Technical availability depends on device model, OS version, access state and acquisition method.
€390 · up to 3 accounts

User-account security analysis

A review of up to 3 client-controlled accounts: authentication events, active sessions, trusted and connected devices, recovery channels, forwarding rules where relevant, MFA configuration, third-party access and OAuth grants, and location-sharing configuration. Reauthentication remains customer-guided.

€149 · €39 each additional

Credential-exposure analysis

Checks of up to 3 client-controlled identifiers (email addresses or phone numbers) against legally accessible known breach and credential-exposure sources, including exposed-data categories and remediation priority where that information is available. An exposure record does not in itself prove device compromise.

€1,290

Integrated forensic review

One device, up to 3 connected accounts and credential-exposure analysis combined into a single defined case with a consolidated report.

Examination scope

Layered analysis of the device, connected accounts and credential exposure

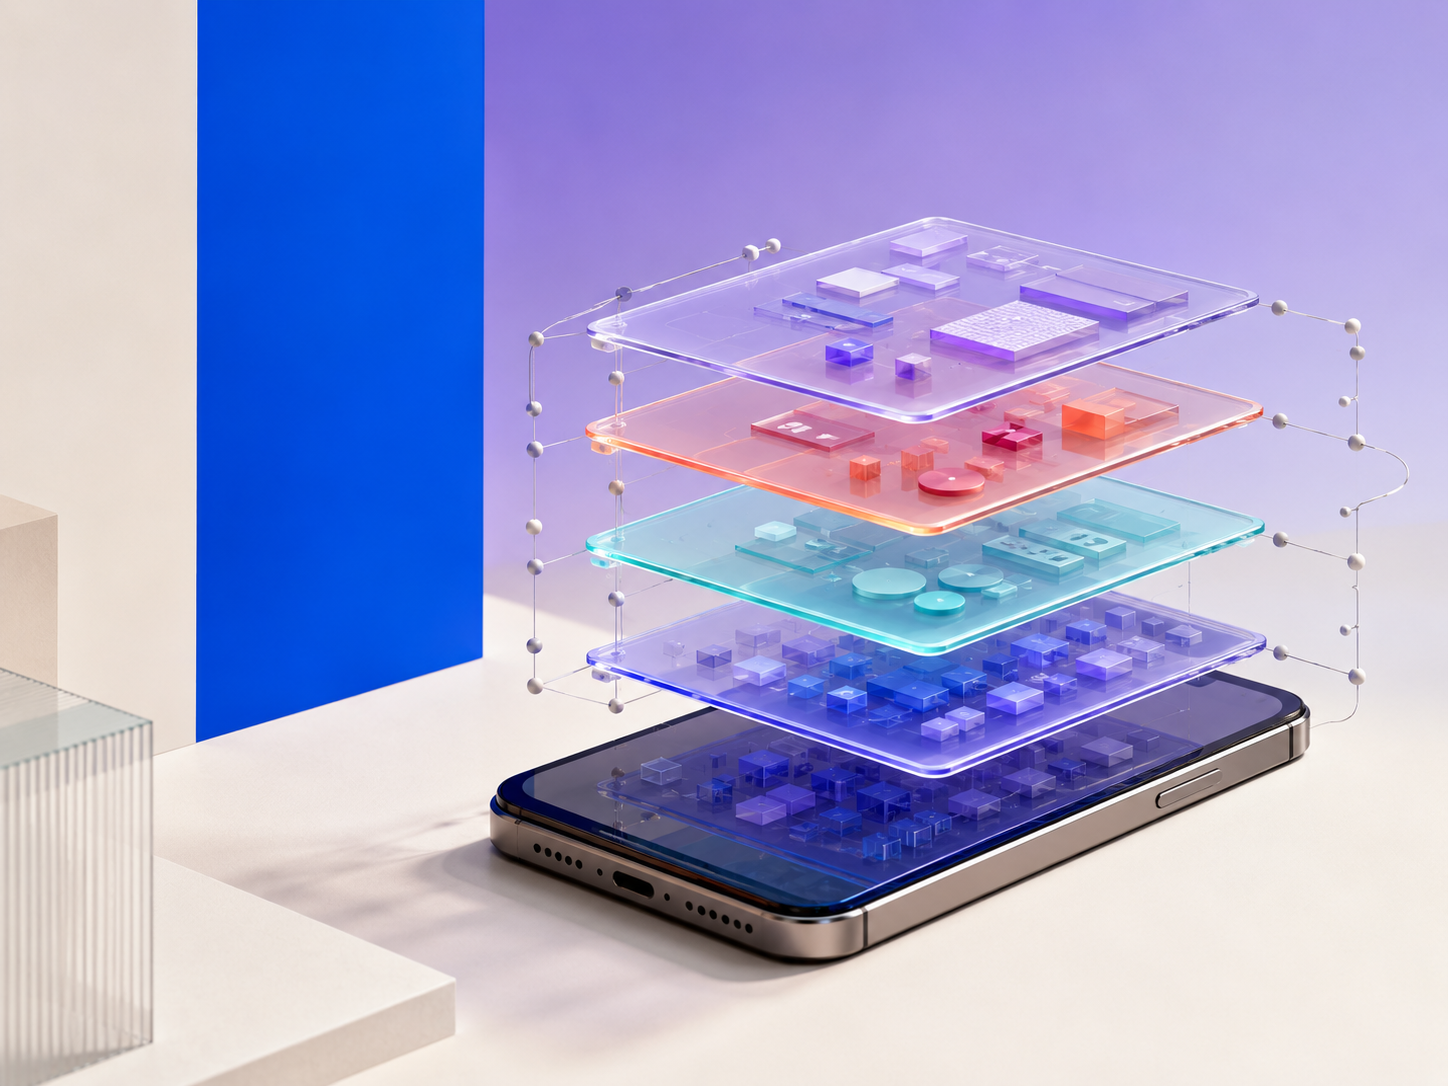
The examination is built in layers: device state and security configuration, system and application artefacts, diagnostic records, and access metadata for connected user accounts. Observations are then correlated into an incident timeline.

The technical availability of each layer depends on the device model, operating-system version, access state and the authorised acquisition method used. Anything that could not be established is recorded as a limitation of the examination, not as a finding.

  • Authorised acquisition within the agreed scope
  • Indicator correlation and incident-timeline reconstruction
  • Findings, anomalies and limitations classified separately
Launch toolset

The launch toolset includes licensed iMazing Business/CLI and Certo alongside the open-source MVT and AndroidQF. Naming a tool implies no vendor approval, endorsement, partnership or guaranteed detection.

Isometric illustration of a mobile device with several translucent layers representing analysis levels
Methodology

Examination methodology

Four stages that apply to every case, whatever the scope. The procedure is documented, repeatable and limited to devices and accounts covered by lawful authority.

  1. 01

    Scope and authority

    We confirm lawful authority, device ownership, the requested examination scope, the relevant period and the evidence-preservation requirements.

  2. 02

    Authorised acquisition and integrity

    We document intake and device state, perform the technically appropriate authorised acquisition or export, maintain chain-of-custody records, and create an evidence manifest with cryptographic hash values where relevant.

  3. 03

    Artefact analysis and correlation

    We examine available system and application artefacts, diagnostic records, configuration and profile state, account-access metadata and applicable indicators. Timestamps, event sequences and cross-source observations are correlated.

  4. 04

    Classification and reporting

    Verified findings, anomalies requiring contextual validation, inconclusive observations and limitations are presented separately, together with an incident timeline, the methodology, evidential references and proportionate remediation recommendations.

No formal laboratory accreditation is implied.

Deliverable

What the technical report contains

The report is the deliverable of every case. It is written in Croatian or English and delivered through a secure expiring download, with the access code sent separately.

The technical report may support consultation with counsel, the police or a court. Legal admissibility and the outcome of any proceedings cannot be guaranteed. An independent reviewer and certified translation are quoted separately.

  • Agreed scope and basis of authority
  • Acquisition and examination method with technical limitations
  • Device and case identifiers appropriate for the report
  • Evidence manifest and hash values where relevant
  • Incident timeline
  • Classified findings with references to the supporting artefacts
  • Account and credential-exposure observations, where included
  • Remediation priorities
  • Secure expiring delivery, in Croatian or English
Preserving traces

Before you hand over or ship the device

This guidance applies from the moment you become suspicious until the device is packed. If your immediate safety requires something different, safety takes priority.

  1. 01

    Do not factory reset the device

    A reset permanently removes the artefacts the examination relies on.

  2. 02

    Do not delete apps

    Removing an app also removes the records that could document it.

  3. 03

    Do not install major system updates

    Major updates change and discard diagnostic records.

  4. 04

    Do not change passwords from the device in question

    If a password must be changed immediately, do it from a separate trusted device.

  5. 05

    Do not confront the person you suspect

    A conversation before the examination usually leads to traces being deleted and can increase the risk to you.

  6. 06

    Power the device off before packing

    Shut the device down fully before packing it according to the instructions you receive when the case is accepted.

Prices

Fixed prices, published up front

Prices are fixed and apply per case. A purchase is conditional on case acceptance; if we decline a case, everything paid is refunded in full.

Mobile-device forensic examination
€790

Targeted artefact examination and an incident timeline for one unlocked, client-owned device.

  • iOS or Android
  • Chain-of-custody records
  • Technical report
User-account security analysis
€390

Up to 3 client-controlled accounts: sessions, trusted devices, recovery channels and OAuth grants.

  • Up to 3 accounts
  • No passwords requested in forms
  • Technical report
Credential-exposure analysis
€149

Up to 3 client-controlled identifiers checked against known breach and exposure sources.

  • Up to 3 identifiers
  • €39 each additional identifier
  • Technical report
Integrated forensic review
€1,290

Device, up to 3 connected accounts and credential-exposure analysis in one case.

  • Device examination
  • Up to 3 connected accounts
  • Credential-exposure analysis

Displayed consumer prices are final.

Add-ons

  • Additional account€95 · 3 for €250
  • Account security hardening after evidence preservation and separate authorisation€109 up to 3 accounts · €229 up to 7 accounts
  • Priority handling+€990
  • Same-phone targeted comparison within two years€490
  • 12-month exposure monitoring, weekly reviewed summary€129 for 3 identifiers · €29 each additional

Terms

  • The 3–7 working day turnaround starts only when the device, signed documents, payment and required access are complete.
  • Priority handling (+€990): final report by the end of the second working day after complete intake and eligibility confirmation.
  • If we miss the priority deadline for reasons within our control, we return the surcharge only: €495 with a completed report, or €990 without a report.
  • Payment: 50% in advance and 50% before the report, by bank transfer or card via a payment link.
  • If usable acquisition is technically impossible, we charge up to €190 for the documented attempt and refund the remainder.
  • If no indicator is found, the agreed price remains payable in full, because the examination itself is the service.
Mandatory assessment

Describe the circumstances of the case

The assessment takes 5 to 7 minutes and is a prerequisite for every case. You see a preliminary indicator level before we ask for any contact details. The level does not change eligibility or price and does not express a probability of compromise.

Start the initial assessment
Interface preview
FAQ

Questions we hear before the first case

Can you tell me for certain that someone is monitoring me?

We can establish whether verifiable technical indicators exist and document them. Their absence within the available dataset is not proof that nothing happened, and their presence does not necessarily mean malicious action. We do not give percentages or probabilities, and we do not attribute responsibility.

What if the examination finds nothing?

The agreed price remains payable because the examination itself is the service, and the report documents what was examined, what was classified as inconclusive and which limitations applied. If usable acquisition is technically impossible, we charge up to €190 for the documented attempt and refund the remainder.

Whose devices do you examine?

Unlocked, client-owned devices. Company-owned devices only with formal written authority. Minors require guardian consent plus age-appropriate child assent, and shared or family devices require the consent of all affected adults. An NDA is available on request.

How does the device reach you?

The device is shipped to Zagreb using the instructions you receive when the case is accepted, or brought in by appointment only after the assessment. We do not offer a walk-in service or remote forensic extraction. Return shipping is included where stated in the final offer.

Services

Mobile-device forensics. Methodical, documented and discreet.

Signum Cyber conducts specialist examinations of iOS and Android devices, connected user accounts and known credential exposures. The review covers relevant system and application artefacts, security configuration, access records and incident-timeline correlation, followed by a clearly structured technical report.